The boundary your organization actually defends
Why an organization is best understood as a boundary — and why most leaders defend the wrong one.
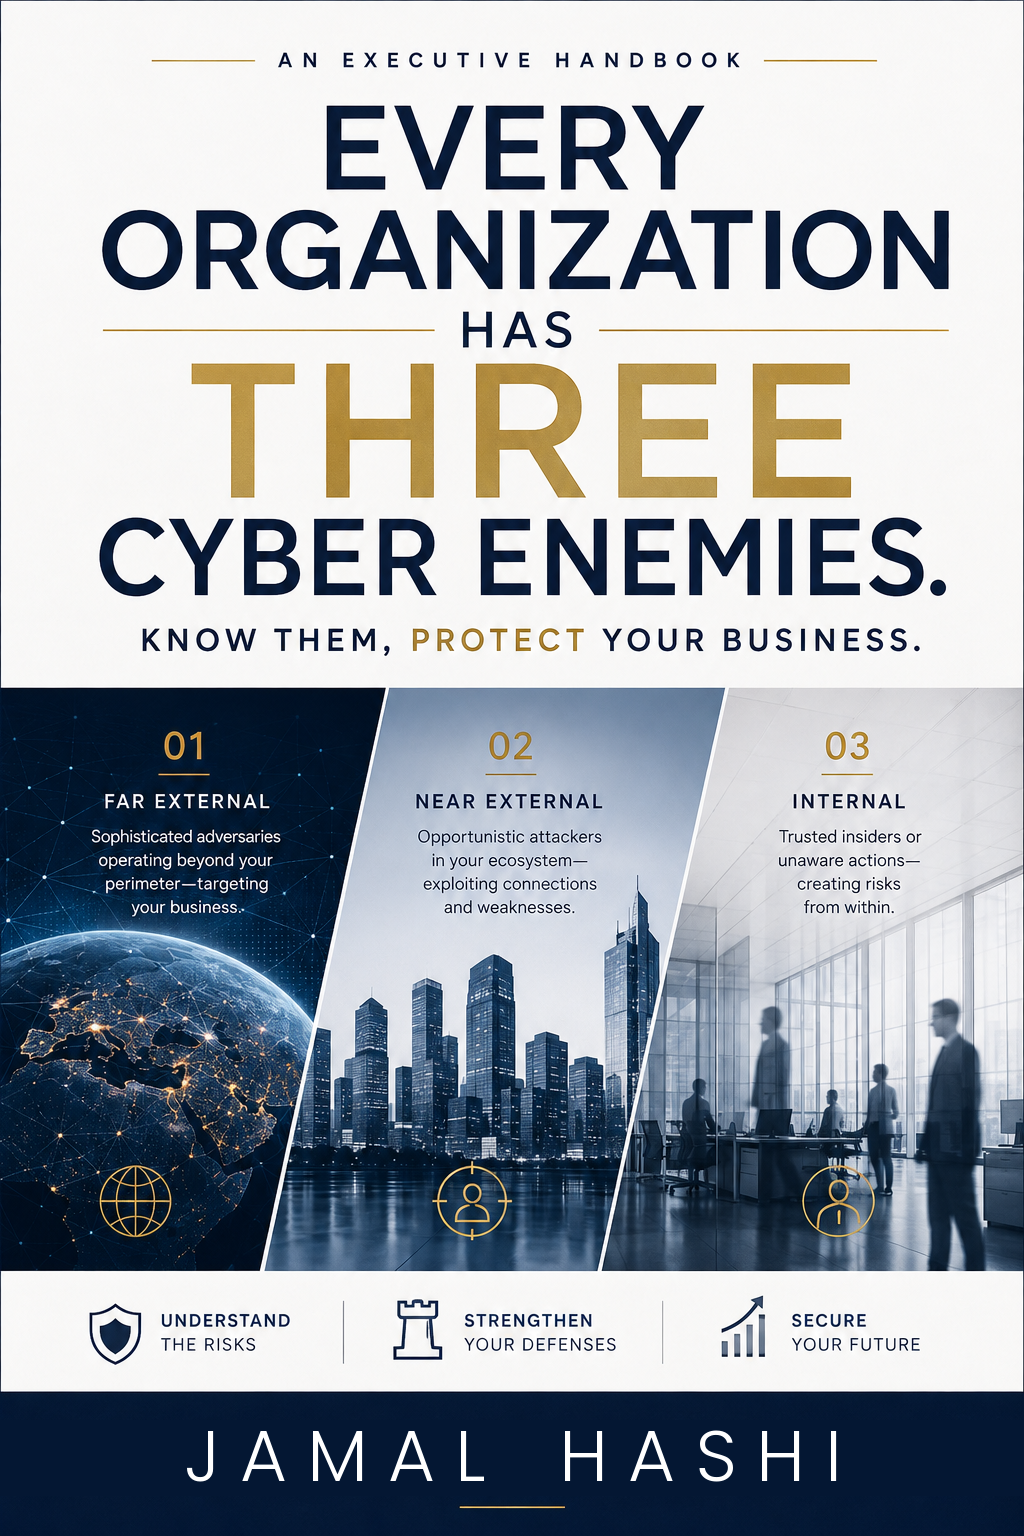
Free executive handbook
Know Them. Protect Your Business.
Most cybersecurity guidance is written for engineers. This handbook is written for the people who carry the risk. In plain language, it explains who is actually testing your organization, where your real boundary sits, and what to do about it.
Free PDF · No spam · Written by Jamal Hashi, founder of CyberPost Advisory
What you'll learn
Each chapter is short, practical and free of jargon — designed to be read in an afternoon and used in your next leadership meeting.
Why an organization is best understood as a boundary — and why most leaders defend the wrong one.
How ordinary employees, contractors and trusted access become the most common route to a breach.
Suppliers, partners and integrations that quietly extend your boundary far beyond your own systems.
Opportunistic external attackers who find you through exposure, not intent — and how they choose targets.
Where accountability breaks down between IT, leadership and third parties, and how to close that gap.
A practical way to ask better questions, judge risk, and direct spend with confidence.
Who it's for
About the author
Founder of CyberPost Advisory, with over 20 years across security engineering, assessment and advisory work. He writes and advises on one question: what can an attacker see, and what does that mean for the business?
More about JamalThe handbook explains the risk. A CyberPost exposure snapshot shows you your own.