About
Security decisions should be based on evidence, not assumption.
CyberPost Advisory is a cybersecurity consultancy focused on external exposure. We help organizations see themselves the way an attacker does, then reduce what that attacker can reach.
How we work
Principles that shape every engagement
Outside-in
We start where an attacker starts: with what is publicly visible, not with an internal inventory that may be out of date.
Evidence, not alarm
Findings are demonstrated and prioritised against business impact. No fear-driven selling.
Authorised by default
Nothing intrusive happens without written authorisation, agreed scope and rules of engagement.
Proportionate
Recommendations match the organization's size, sector and obligations — not a generic maximum.
Clarity for two audiences
Every engagement produces both an executive narrative and technical detail engineers can act on.
Continuity
An attack surface is not a snapshot. We help organizations keep watching after remediation.
Meet the founder
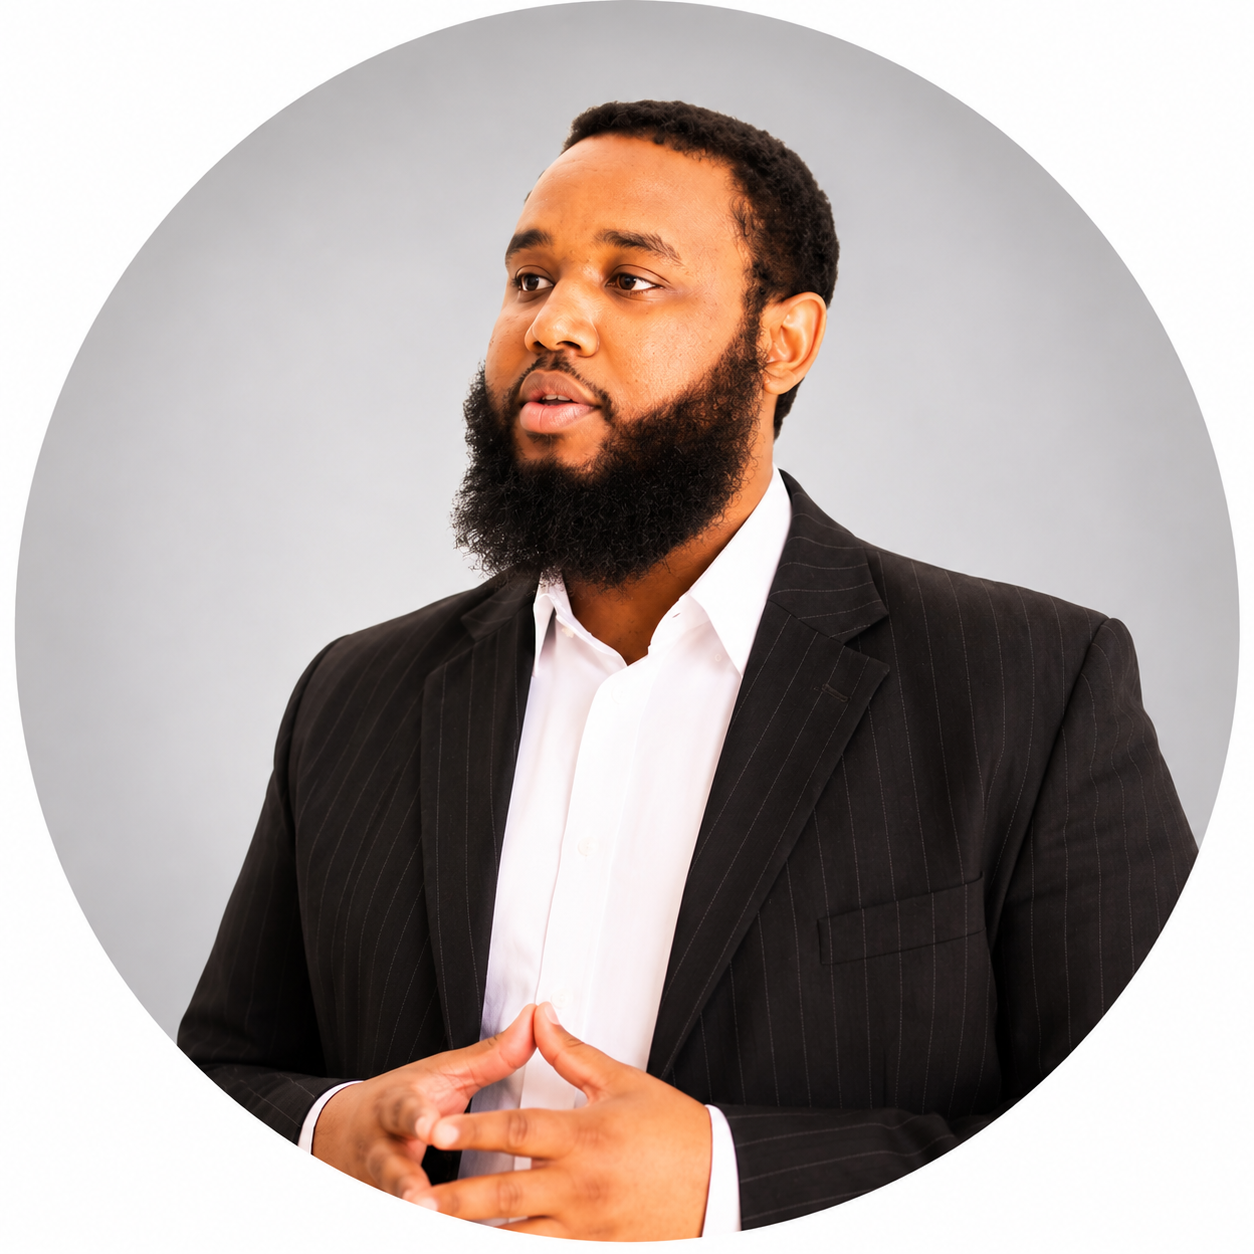
Jamal Hashi
20+ Years
Cybersecurity & security research
Founder & CEO · Cybersecurity Analyst · Security Researcher
Jamal Hashi is the Founder and CEO of CyberPost Advisory, with more than 20 years of experience in cybersecurity and security research.
His experience spans penetration testing, red teaming, vulnerability research, ethical hacking, bug bounty hunting, threat intelligence, OSINT, attack-surface analysis, and security assessments.
His work sits at the intersection of technical security and business decision-making. He believes cybersecurity should not be treated as a purely technical issue belonging to IT, but as a business, operational, financial and strategic concern.
Through CyberPost Advisory, Jamal helps organizations understand what an attacker can discover, reach and potentially exploit from the outside — and translates those findings into clear, actionable intelligence for executives, business leaders and security teams.
“You cannot effectively defend against a threat you do not understand.”
What can an attacker see?
What can an attacker see, discover, exploit and ultimately use against your organization?
CyberPost Advisory works from the outside in — exposed assets, publicly available information, weaknesses and viable attack paths — and shows how seemingly unrelated pieces of information can be connected by an attacker into a route into your business.
Founder expertise
Where that experience is applied
- Cybersecurity Strategy & Advisory
- Penetration Testing
- Red Teaming
- Vulnerability Research
- Security Research
- Ethical Hacking
- Bug Bounty Hunting
- Threat Intelligence
- OSINT
- External Attack Surface Management
- Web & Application Security
- Security Assessments
- Cyber Risk
- AI & Cybersecurity
- Emerging Cyber Threats
- Executive Cybersecurity Education
Author
Every Organization Has 3 Cyber Enemies. Know Them. Protect Your Business.
An executive-focused guide to understanding the fundamental categories of cyber threats facing modern organizations and the principles business leaders need to understand to better protect their people, systems, data and business.
Responsible testing
Active security testing is only performed with written authorisation from an authorised representative of the organization, within a defined scope, under agreed rules of engagement, and with appropriate safeguards. Passive exposure review uses only publicly available information.
Let's find out what your organization is exposing.
One assessment. A clearer understanding of your external risk.